Aadhaar Masking: What RBI-Regulated Entities Must Redact, and When
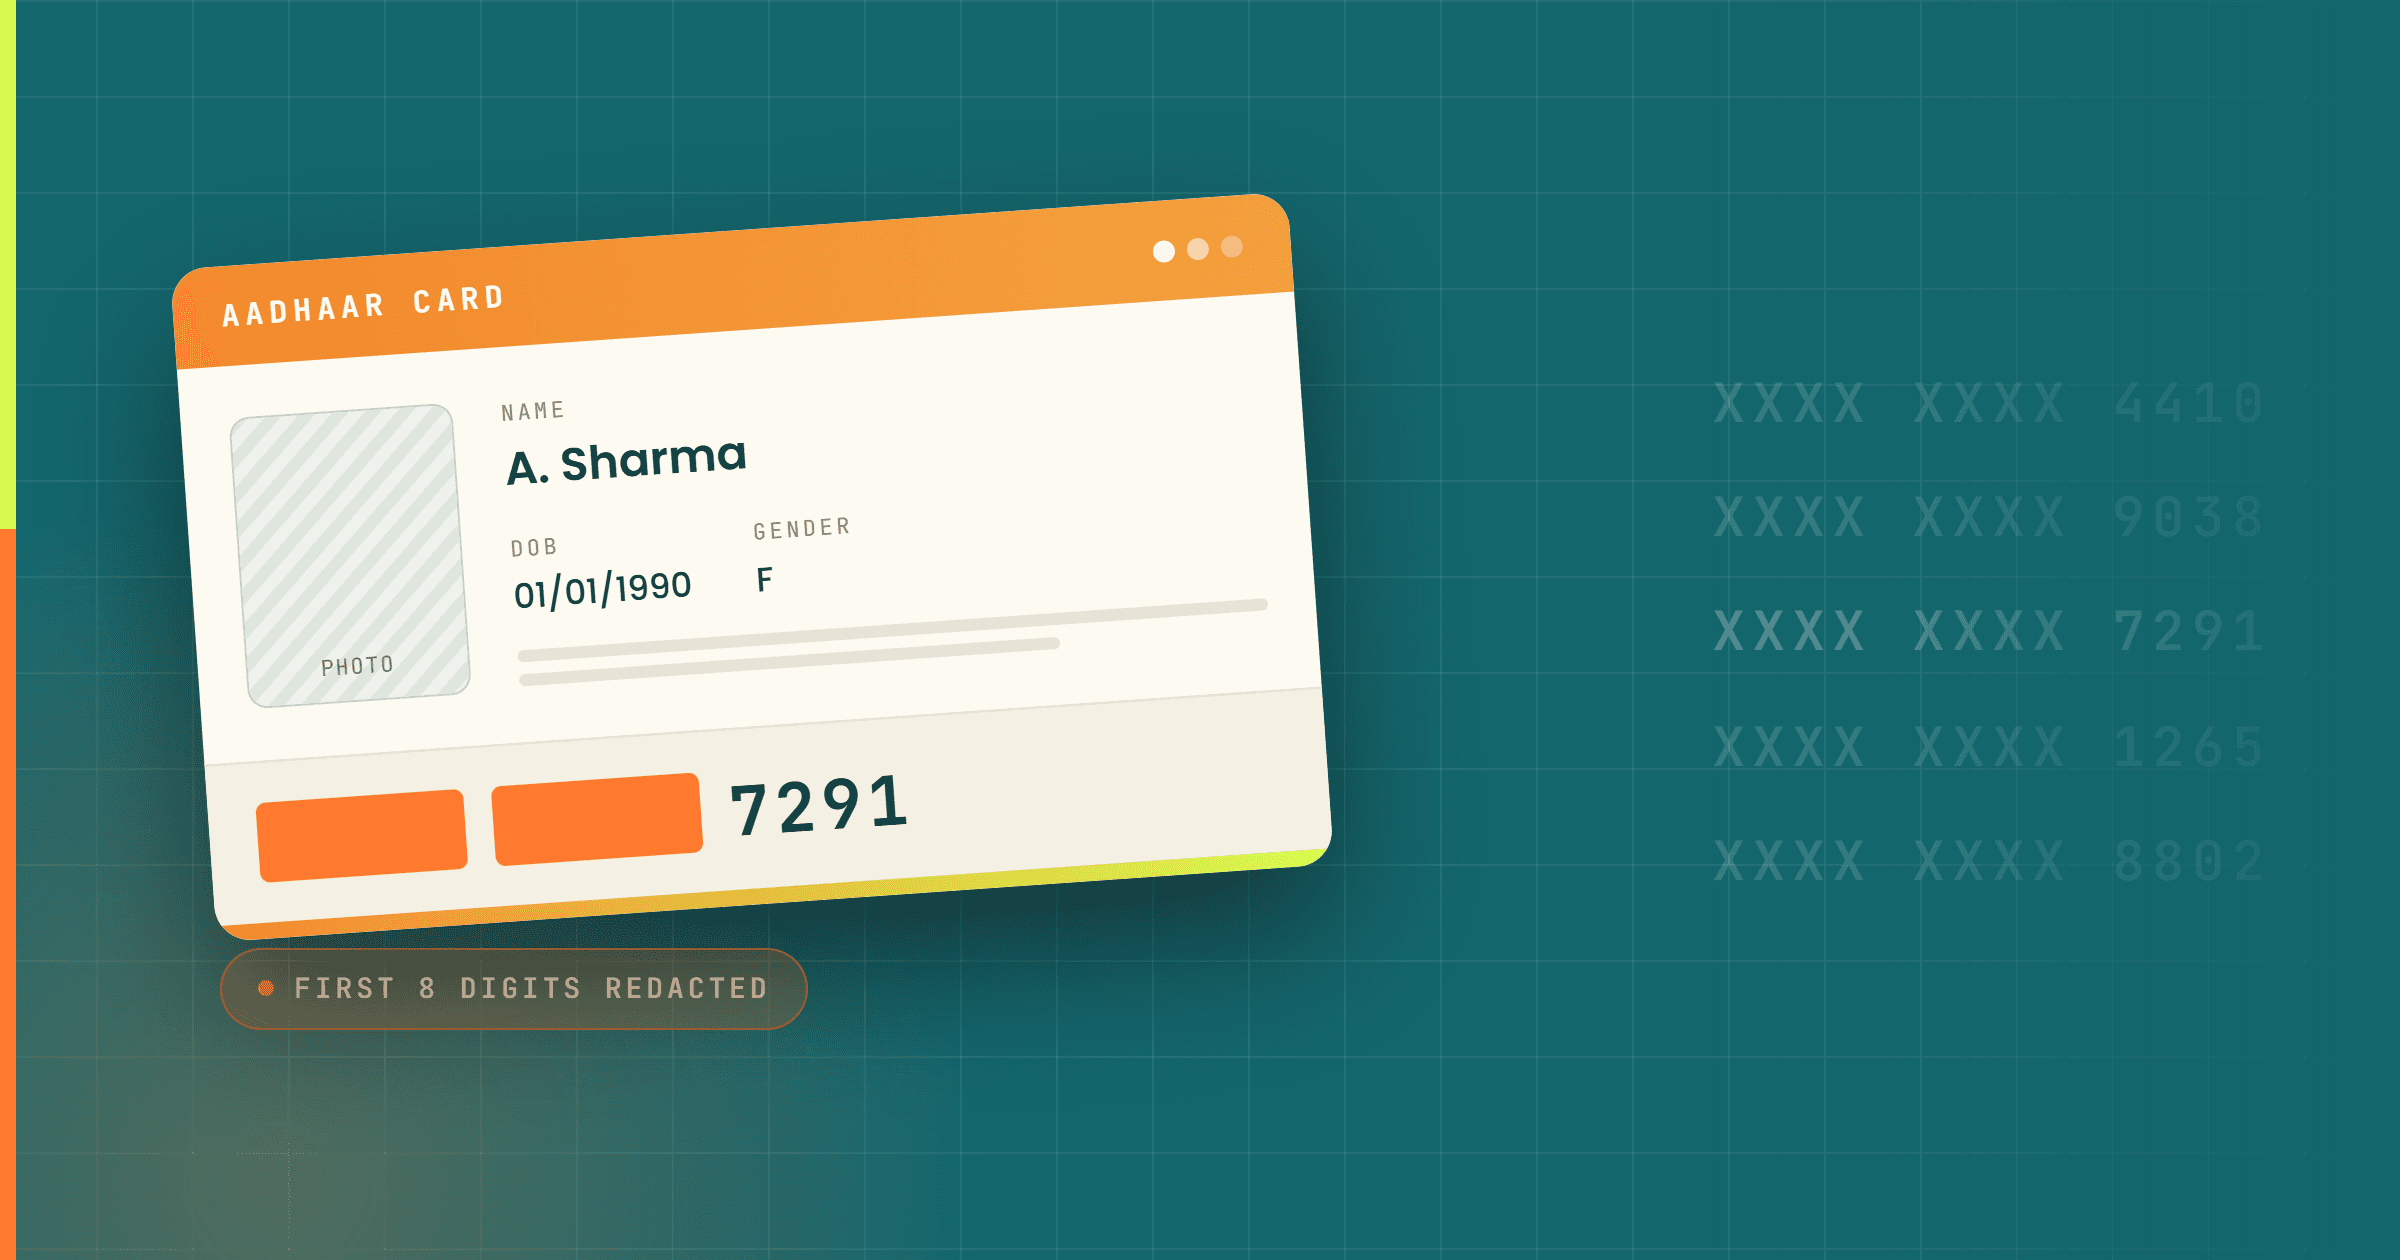
Of every document in a customer file, the Aadhaar copy is the one Indian law treats on separate terms. A bank, NBFC or insurer that stores one holds a number the statute restricts in ways it restricts no other identity proof. Aadhaar masking is the control written for that problem: the first eight digits are removed before the image reaches permanent storage, and the last four stay legible. Most vendor guidance presents the duty as broader and more recent than the text supports. What has genuinely moved is the framework carrying it. The Reserve Bank replaced the 2016 Master Direction on KYC with entity-specific Directions on 28 November 2025, which leaves an institution still working from the 2016 text reading a document that no longer governs it.
Aadhaar masking, as UIDAI defines it
UIDAI leaves little room for interpretation. Masked Aadhaar, in the Authority's FAQ, "implies replacing of first 8 digits of Aadhaar number with 'xxxx-xxxx' while only last 4 digits of the Aadhaar Number are visible." Everything else on the document survives: name, date of birth, gender, address and photograph are untouched.
So does the QR code, which several vendor pages get wrong. UIDAI's Secure QR code carries the Authority's digital signature, and the record inside it holds the last four digits along with the holder's name, address, gender, date of birth and photograph. Redaction touches the printed number field and nothing else, so the code remains scannable. Pages claiming that masking blanks the QR are describing something UIDAI's own documentation contradicts. If the claim held, offline verification against a masked copy could not work at all.
Three separate things travel under the same phrase, and conflating them muddies most discussions of the obligation. A holder can download a masked Aadhaar from myAadhaar or DigiLocker by selecting the masked option and hand that over. Separately, a reporting entity redacts a copy it has already collected, and this is the institutional duty. Offline eKYC is a third case entirely: the Aadhaar XML or Secure QR record is built to carry only the last four digits, so no full number reaches the entity to be redacted.
Where the duty actually originates
Authority for the Aadhaar redaction duty starts in the Prevention of Money-Laundering Act, 2002, and passes through the PML (Maintenance of Records) Rules, 2005. Only at the end of that sequence does it reach RBI's Directions. The operative text is Rule 9(16):
Every reporting entity shall, where its client submits a proof of possession of Aadhaar Number containing Aadhaar Number, ensure that such client redacts or blacks out his Aadhaar number through appropriate means where the authentication of Aadhaar number is not required under sub-rule (15).
The construction has two operational consequences. Responsibility sits with the reporting entity while the physical act belongs to the client, since the entity must ensure the client redacts. In practice institutions discharge this by masking at capture. A customer sliding a photocopy across a branch counter is not going to black out eight digits unprompted, and the consequence lands on the entity regardless.
Then there is the carve-out, which published guidance almost never mentions. Under clause (a) of sub-rule (15), a banking company authenticates a submitted Aadhaar number through UIDAI's e-KYC authentication facility, as does a reporting entity notified under the first proviso to sub-section (1) of section 11A of the PMLA. Where that clause requires the authentication, the redaction duty in sub-rule (16) does not attach at all. An entity running Aadhaar OTP e-KYC on a notified basis therefore occupies a different position from one that files a photocopy as an officially valid document.
A good deal of published material credits the masking mandate to an RBI amendment dated 29 May 2019. That inverts the actual chain of authority. RBI's Directions bring a statutory duty into the supervised sector by restating it, which means an entity that satisfies the Direction but ignores the rule still answers to the rule.
The 28 November 2025 rewrite
The 28 November 2025 tranche split one Master Direction into ten, each of them updated as on 29 December 2025. Seven cover banks: commercial banks, small finance banks, payments banks, local area banks, regional rural banks, urban co-operative banks and rural co-operative banks. Outside banking there are three more, issued for NBFCs, all-India financial institutions and asset reconstruction companies. A commercial bank now reads RBI/DOR/2025-26/169. For an NBFC the number is RBI/DOR/2025-26/361.
Redaction came through the rewrite intact, carried as an Explanation to the customer due diligence paragraph. The Commercial Banks Directions place it at paragraph 23, Explanation 1: "The bank shall, where its customer submits a proof of possession of Aadhaar Number containing Aadhaar Number, ensure that such customer redacts or blacks out his Aadhaar number through appropriate means where the authentication of Aadhaar number is not required as per proviso (i) above." Proviso (i) is that paragraph's e-KYC authentication route.
Numbering diverges from one Direction to the next. A compliance team is better served reading the Direction issued for its own licence than a generic summary, because the commercial bank text is not universal and a citation lifted from it will not survive scrutiny at an NBFC or a co-operative bank. What follows is guidance on how the framework fits together, not legal advice on whether a particular configuration satisfies a supervisor.
Asset reconstruction companies
ARCs are now a named category with a Direction of their own, the Reserve Bank of India (Asset Reconstruction Companies – Know Your Customer) Directions, 2025, RBI/DOR/2025-26/377, issued in that same 28 November 2025 tranche. No ARC-specific Aadhaar masking standard came with it. The ARC text carries the same Explanation at paragraph 22, and its V-CIP paragraph points back to it at 26(2)(vii). For ARCs, what changed is where the duty is read. The demand itself is unchanged.
Aadhaar Act limits that sit alongside the KYC duty
The PML Rules govern the Aadhaar copy sitting in the KYC file. Everywhere else the number has travelled, it is the Aadhaar (Targeted Delivery of Financial and Other Subsidies, Benefits and Services) Act, 2016 that applies, and holding that wider perimeter is the harder task. Section 29(4) provides that no Aadhaar number, demographic information or photograph collected or created under the Act in respect of an Aadhaar number holder "shall be published, displayed or posted publicly, except for the purposes as may be specified by regulations."
Section 33A attaches a price to that. An entity in the Aadhaar ecosystem that fails to comply with the Act, with rules or regulations made under it, or with directions issued by the Authority under section 23A is liable to a civil penalty extending to one crore rupees for each contravention. A further penalty extending to ten lakh rupees runs for every day the failure continues after the first. Adjudication under section 33B falls to an officer of the Authority not below the rank of Joint Secretary to the Government of India, acting on a complaint by the Authority.
Exposure rarely originates in the KYC file itself. It comes from the unredacted copy that escaped it. An image sitting on an onboarding email thread is one route. A screenshot attached to a support ticket is another, and an outsourced processor's staging bucket is the one an institution tends to have least visibility into. A masking programme scoped to the document store reaches none of them.
The 2022 advisory, correctly stated
On 27 May 2022 the Press Information Bureau carried a release, PRID 1828797, advising the public against sharing a photocopy of Aadhaar with any organisation and recommending a masked Aadhaar instead. Two days later it was withdrawn, in view of the possibility of misinterpretation, and UIDAI restated the position as one of exercising normal prudence in using and sharing Aadhaar numbers (PIB PRID 1829162). Vendor pages continue to quote the first release as though it were a live prohibition, without the second. Neither release created an obligation for a regulated entity. That obligation sits in Rule 9(16).
Applying Aadhaar masking in an onboarding flow
Placement is the design decision that matters most when an institution fits masking into an existing identity verification flow in India. Aadhaar number masking applied at the point of capture, before the image reaches permanent storage, means no unredacted copy ever exists for anyone to find later. Push the same operation into a batch job and the original has already been stored, replicated into backups and possibly indexed, so remediation has to chase every one of those copies.
That gives two operating modes. Real-time masking sits in the capture path and works to a latency budget of a second or two. Bulk masking runs across an archive, where throughput is the constraint and latency is irrelevant. Almost any institution with some history behind it carries a legacy population of customer proof images filed before masking was operationalised. Those images are unsegregated, and nothing in the metadata says which of them contain an Aadhaar number. Sizing that population is usually the harder half of the exercise.
In practice the formats run to PDF, JPG, PNG and TIFF, scans of scans included. The useful questions to put to a vendor concern the cases where layout-dependent detection breaks down. An Aadhaar page buried inside a composite multi-document PDF is one. So is a number handwritten into a form field, or a photocopy of a photocopy where the digit strokes have broken up. Enrolment slips present the number in a layout a detector may never have seen. Accuracy figures published by masking vendors, this one included, are self-reported and generally arrive with no disclosed methodology, test corpus or false-negative rate, which makes any two of them non-comparable. Recall on the awkward cases is the better question.
Masking and V-CIP
Redaction only becomes necessary because a full Aadhaar number was collected. The V-CIP identity routes are, in part, a way of never collecting one. Paragraph 27(2)(vi) of the Commercial Banks Directions permits four routes to identity inside a video session: OTP-based Aadhaar e-KYC authentication, offline Aadhaar verification, a KYC record downloaded from CKYCR against the customer's KYC identifier, or an equivalent e-document of an officially valid document, including one drawn from DigiLocker. Paragraph 27(2)(vii) then directs the bank to redact or blackout the Aadhaar number in terms of paragraph 23. Every entity's Direction carries that cross-reference. Offline verification comes with a freshness condition at 27(2)(viii), which requires that the XML file or Aadhaar Secure QR code generation date be no older than three working days from the date of the V-CIP. A printed copy of an equivalent e-document is not valid at all, and that includes an e-PAN (27(2)(xii)).
Set against Rule 9(16), those routes separate cleanly. Authentication sits inside the sub-rule (15) position. Offline verification returns a record holding only the last four digits, so nothing arrives that needs redacting in the first place. The obligation is created by the remaining route, the one that ends in a stored image of an Aadhaar letter. KYC Hub's identity verification layer draws Aadhaar details through DigiLocker, where the customer logs in and gives consent for the details to be fetched directly, and through the Secure QR code, where the XML data is read from an Aadhaar image rather than requiring the number to be captured and stored as a document. Conduct of the session itself remains with specially trained officials of the regulated entity.
Groups holding more than one licence
A bank with an NBFC subsidiary, or a lender with a payments arm, has almost certainly been running a single KYC policy drafted against the 2016 Master Direction and applied uniformly across the group. That one document now has to map onto several Directions whose numbering diverges and whose requirements, in places, diverge as well. The redaction Explanation makes a convenient test of whether the mapping has actually been done. An institution able to produce, for every licence it holds, the paragraph of its own Direction that carries the duty alongside the control discharging it has finished the work. Citing paragraph 23 across the board is a sign the work has not begun.
See how KYC Hub applies masking at the point of capture, before an unredacted image ever reaches storage. Book a walkthrough of KYC Hub's identity verification layer — DigiLocker retrieval and Secure QR extraction, under one audit trail.